What a day yesterday was for crypto.
If you missed it, Thursday morning the parent company of the New York Stock Exchange announced an investment in Trade(XYZ), the company responsible for Hyperliquide’s perpetual shares, as well as plans to bring criminals to the United States. Hours later, in an event of strange irony, Binance, the world’s largest cryptocurrency exchange and arguably Hyperliquid’s main rival, suffered the largest cryptocurrency hack on record and, by some accounts the largest theft in history.
The stock market estimates the damage at $6.3 billionwhich is more than four times the amount stolen in the infamous Bybit hack last year.
Binance insists that customer funds are safe and will cover losses. But with billions missing, withdrawals suspended, and questions about how it happened, the concern is obvious: If Binance isn’t safe, what is?
Let’s break down exactly what we know so far and where we go from here.
— (@)
According to Binance’s preliminary investigation Posted late last night, the exchange initially traced the attack to a compromised DevOps engineer’s laptop, which apparently gave the attacker access to internal systems that could authorize withdrawals. How the laptop was compromised remains unclear, and Binance says additional points of compromise have been found.
— (@)
Co-CEO Richard Teng has since explained that the operation involved multiple attackers, who also used a self-destruct mechanism to erase evidence as they went along.
Well, if they allowed withdrawals, they must have obtained private keys, right? It doesn’t look like that.
On Ethereum, security company TRM Labs discovered that the attacker had valid, signed permissions under an Ethereum feature called EIP-7702, allowing a Binance wallet to hand over control to malicious code. According to Teng, this happened without passing Binance’s normal approval checks. In effect, they could ask the wallet to send funds elsewhere without necessarily stealing its private key. How these signatures were obtained remains unknown.
But that only explains Ethereum. According to TRM, nine other blockchains, including Bitcoin and Solana, were also depleted by normally signed transactions, suggesting a broader compromise in Binance’s withdrawal approval systems.
Not good.
As one might have suspected, it appears that North Korea was behind the attack.
TRM and chain analysis have linked the attack to the North Korean group TraderTraitor, responsible for the $1.5 billion Bybit hack last year. Binance has not confirmed the identity of the attackers and is allegedly worked with the FBI and US Secret Servicealongside other law enforcement agencies around the world.
Do you like this article?
Subscribe to Bankless or log in
— (@)
Deposits are operating normally, but withdrawals on the exchange remain suspended during a security overhaul, although Binance expects them to resume by Sunday (fingers crossed). It reviews everything from employee devices and cloud systems to private key management and transaction signing procedures before putting withdrawals back online.
Industry partners including Tether and Circle helped freeze approximately $3 billion in affected assets, according to Binance. This is encouraging, even if frozen funds are not necessarily recovered funds. However, other stolen assets, like bitcoin and ether, have no transmitter capable of freezing them. Aave has temporarily frozen new deposits and borrowings on its markets to avoid further abuses, before frost lifted Friday morning.
The immediate concern, of course, is whether Binance can make its customers whole. It promises to cover any losses using its Secure Asset Fund for Users (SAFU) emergency fund and company cash. Even though SAFU holds around $1 billion, Binance said it has reserved more than $6.34 billion, including $5 billion already held in the affected tokens, and is buying the rest.
— (@)
This is progress, but until Binance can show that customer balances are fully collateralized again, it’s probably too early to jump for joy.
What may provide some comfort (or more concern depending on who you are) is knowing that this is not Binance’s first major security incident.
In 2019, pirates trust 7,000 BTC of the exchange, a loss that Binance fully covered via SAFU.
Obviously, this incident is on a completely different scale and comes at a difficult time.
For an industry still striving to earn the trust of investors and traditional institutions, seeing billions disappear from its largest exchange is hardly reassuring. Especially the day Wall Street announced another major step towards the introduction of Hyperliquidity in the United States.
But the question looming over this incident is a difficult one: If even Binance, with its enormous resources and security infrastructure, is vulnerable to an attack of this magnitude, where exactly are users supposed to feel safe? It’s a valid concern, even if it’s the one that stings the most in the eye of the storm.
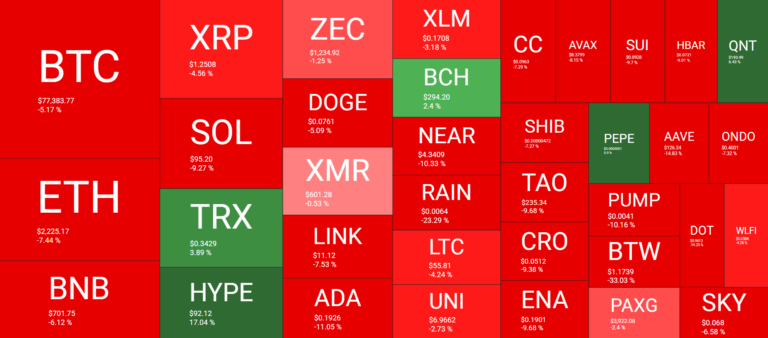
Crypto was already navigating an increasingly challenging market environment, with pressure on tech stocks, broader economic uncertainty and the approach of the US midterm elections. All the while, it held up impressively, until the Binance hack added another reason for investors to sell.
Yet BTC and many of the popular coins in this cycle are only down single digits. In the land of technology, Intel is down almost 30% on the day. For anyone without cash, this kind of relative strength is worth watching.
— (@)
I don’t think this is something crypto can’t recover from. We have already survived major currency collapses, exploits and many other crises. But that could mean more pain, or at least a break.
For now, Binance’s ability to honor its commitments matters more than anything else. Replenishing reserves and explaining what happened are essential to rebuilding trust. I would give it the weekend to see what happens, especially if Binance keeps its promise to reimburse users.
About the Author