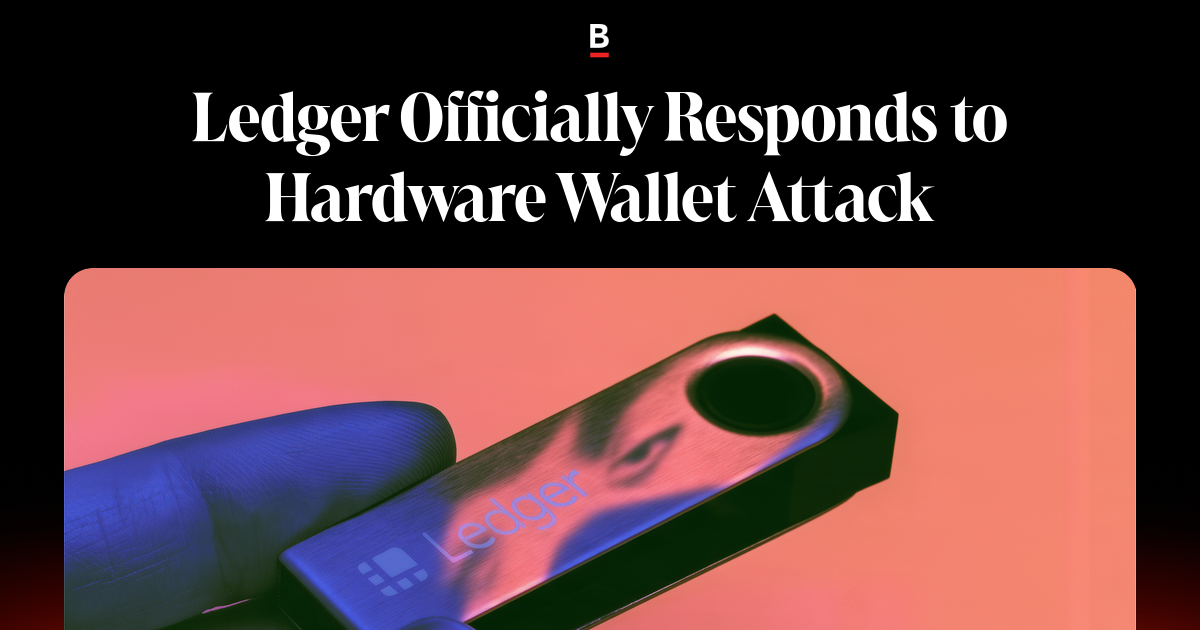
Company announces new security measures for resellers after criminals implanted hidden components in hardware wallets to steal recovery phrases.
Ledger claims that attackers implanted hidden components in real hardware wallets to steal users’ recovery phrases, leading to new security measures and a suspension of regional sales.
What’s the scoop?
-
The attack: In his last disclosureLedger claims that an organized criminal group spent months purchasing genuine devices, installing hidden components designed to steal users’ recovery phrases during installation, and redistributing them through resellers in Southeast Asia.
-
Millions stolen: THE implants captured users’ 24-word retrieval sentences and transmitted them over cellular networks, allowing the attackers to empty their wallets. Estimate from Onchain researchers losses of up to $93 million across more than 300 wallets, although Ledger has not confirmed the total.
-
Ledger’s response: The company requested from authorized resellers and distributors in Southeast Asia and Hong Kong to suspend sales during the investigation. It also inspected devices in stores and warehouses, including in Germany, and reported that all samples examined were clean.
-
Enhanced security: The ledger is introduction of new requirements for resellersincluding keeping devices off store shelves and immediately reporting suspicious products, while strengthening its current ban on reselling returned devices. Importantly, Ledger claims its chips, operating systems and servers were never compromised, with the attack instead exploiting its distribution network.
David Christophe
737 posts
David is a writer/analyst at Bankless. Before joining Bankless, he worked for a series of early-stage crypto startups and with grants from the Ethereum, Solana and Urbit foundations. He graduated from Skidmore College in New York. He currently lives in the Midwest and enjoys NFTs, but no longer participates in them.
About the Author